
Security & Compliance
Security by design: Less data, maximum protection.
Built specifically for union agreement administration and complex bonus schedules. We eliminate high-risk financial data intake, enforce tenant isolation, and mandate two-person approval controls to safeguard payroll funds.
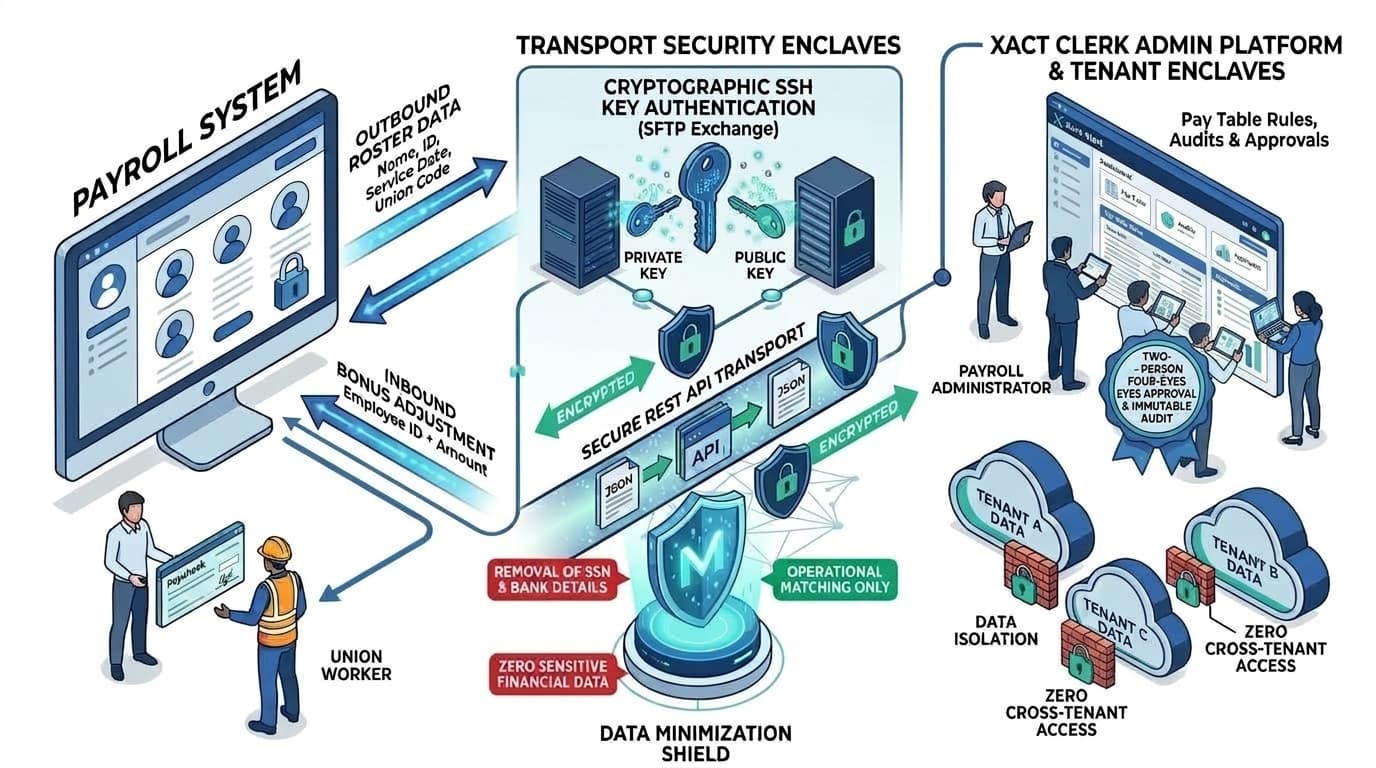
Architectural Overview: High-risk data elimination, tenant-isolated storage, cryptographic transport, and outbound identifier anonymization.
1. High-Risk Data Minimization (The Least-Privilege Standard)
Traditional payroll software collects everything, creating massive liability for IT teams. Xact Clerk operates under the strict principle of least privilege: we never request, process, or store sensitive financial identifiers, government IDs, or personal contact records.
What We NEVER Collect or Store
- ✕Social Security Numbers (SSNs) or Tax IDs
- ✕Bank Account, Routing, or Direct Deposit Details
- ✕Employee Home Addresses, Phone Numbers, or Personal Emails
- ✕Dates of Birth (DOB) or Dependent Information
- ✕Total Compensation, Base Salary Rates, or Tax Withholdings
- ✕Medical, Benefit, or Insurance Records
Minimal Operational Fields Required
- ✓Employee Full Name (for Payroll Admin roster verification)
- ✓Employer Employee Identifier (Badge / Employee ID)
- ✓Service / Longevity Date (to calculate milestone tiers)
- ✓Union Code (to map negotiated contract rules)
2. Flexible & Isolated Transport: SFTP or REST API
Whether your municipal IT environment relies on scheduled batch file transfers or modern event-driven API integrations, Xact Clerk ensures complete cryptographic segregation.
- Asymmetric SSH Keys: Mandatory RSA-4096 or Ed25519 key authentication. Password authentication is prohibited.
- Dedicated Storage Containers: Every customer receives three isolated containers (
xfer-in,xfer-out,xfer-ack). - Scheduled Exposure Windows: Endpoints are closed outside active operational exchange windows.
- Mutual TLS (mTLS): Two-way cryptographic certificate validation before any connection opens.
- OAuth 2.0 Scoped Tokens: Ephemeral, short-lived JSON Web Tokens (JWT) strictly restricted to bonus calculation scopes.
- HMAC Signatures: Webhook payloads use SHA-256 signatures to guarantee origin integrity and prevent replay attacks.
3. Dual-Control Fiscal Governance (Four-Eyes Rule)
Union payroll requires ironclad separation of duties to prevent fraud and calculation errors.
Two-Person Approval Rule
Activating or modifying a union pay table requires submission by one authorized administrator and independent approval by a second administrator. No single user can alter calculations unilaterally.
Append-Only Audit Trails
Every calculation run, approval, file upload, export, and configuration edit is immutably logged with actor identities, timestamps, and verifiable state diffs.
4. IT & Security Quick-Reference Fact Sheet
Common technical specifications for enterprise security reviews and vendor risk assessments:
| Data Residency | 100% United States sovereign cloud regions |
|---|---|
| Data Encryption at Rest | AES-256 encryption on all databases and file storage |
| Data Encryption in Transit | TLS 1.3 (Web / REST APIs), SSHv2 (SFTP) |
| Firewall Requirements | Outbound TCP Port 22 (SFTP) or Outbound TCP Port 443 (HTTPS / API) to Azure West US 2 |
| Outbound Destination | xactclerkprodfiles.blob.core.windows.net |
| Administrative Authentication | Mandatory Multi-Factor Authentication (MFA / TOTP) |
| Tenant Isolation | Isolated AES-256 storage containers and row-level database segregation |
| Outbound File Format | Anonymized Employee ID + Calculated Bonus Code / Amount (Zero employee names) |
Have questions for your IT or Security review?
Request our vendor security packet or talk directly with our engineering team.